

Enterprise AI Solutions: A Complete Guide for IT Teams

Enterprise AI has crossed the line from curiosity to budget line item, but the story is scaling failure. McKinsey's 2025 survey found that nearly two-thirds of organizations had not yet begun scaling AI across the enterprise, while ISG reported that only 31% of studied use cases reached full production in 2025, even though that was still a sharp jump from the prior year. That gap matters because the market isn't stuck on awareness anymore, it's stuck on governance, integration, and operating discipline.
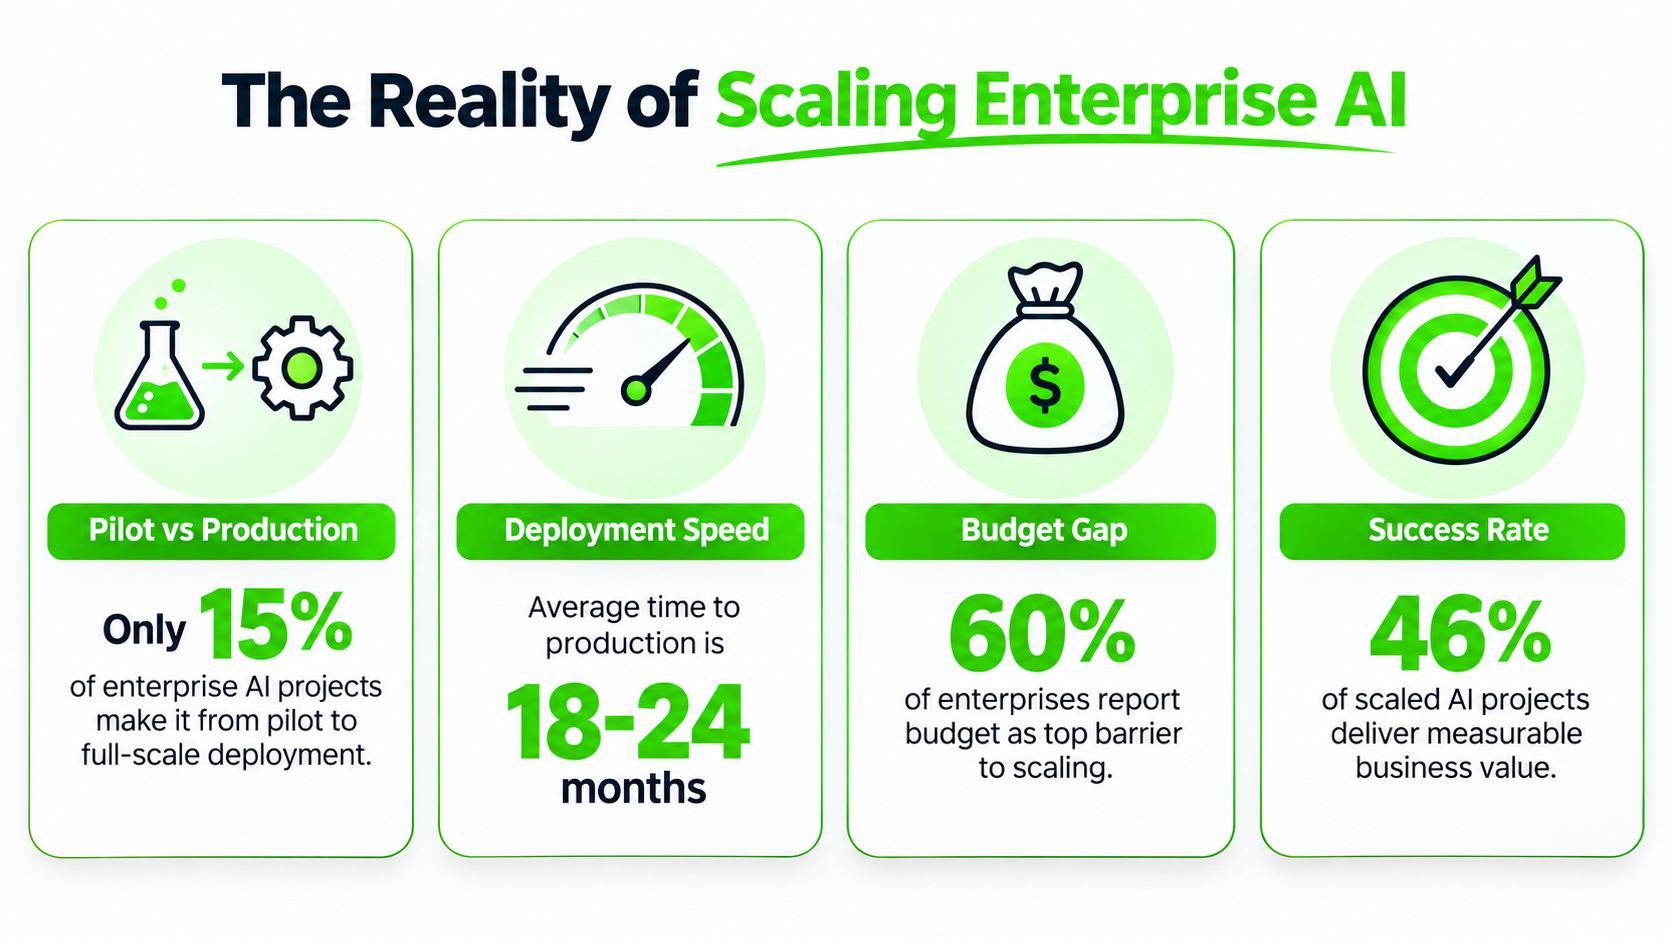
A lot of leaders still talk about enterprise AI solutions as if the hard part is picking a model. In practice, the hard part is getting AI to survive contact with identity systems, legacy workflows, data access rules, and production support teams. Adoption breadth is high, McKinsey-based reporting in 2025 said 88% of organizations were using AI in at least one function, and the EU's official statistics showed 13.48% of enterprises with at least 10 employees used at least one AI technology in 2024. The challenge is no longer basic legitimacy, it's operational control, and that changes how CIOs should buy, design, and govern these platforms.
Table of Contents
Scaling Enterprise AI: Why Most Pilots Don't Reach Production - Adoption is broad, production is selective - What scaling really means
Core Components of Enterprise AI Architecture - What Scaling Actually Entails - Start with the workload, not the brand - Storage matters more than most teams expect
Governance and Compliance in Regulated Industries - Agentic workflows need control points - Legacy workflows are part of the problem
Defining Use Cases and Vendor Integration Criteria - The use case test - Compare vendors on integration depth
Real-World Deployments and Operational Impact - What successful deployment looks like
Proving ROI and Measuring Success - Measure what the business actually feels - Build the CFO view early
Scaling Enterprise AI: Why Most Pilots Don't Reach Production
Enterprise AI usually breaks down after the pilot succeeds, when the work shifts from experimentation to operations. That is the point where ownership becomes vague, approvals slow down, and the system has to fit identity controls, legacy workflows, data access rules, and production support all at once. McKinsey's 2025 AI survey coverage found that nearly two-thirds of organizations had not yet begun scaling AI across the enterprise, while ISG reported that only 31% of studied use cases reached full production in 2025. The market has moved past curiosity, but consistency is still missing.
Adoption is broad, production is selective
CIOs feel pressure because adoption can look healthy in one part of the business while the rest of the enterprise is still waiting on governance, integration, or a secure data path. Teams get a working use case into one function, then hit a wall when another group needs the same capability under different controls. AI may be present, but it is not yet normalized across the enterprise.
Practical rule: if a use case cannot pass security review, fit the existing workflow, and survive handoff to operations, it is still a pilot no matter what the demo says.
The broader adoption numbers make the gap harder to ignore. Many organizations are using AI somewhere, but that does not mean they have built the operating model needed for repeatable deployment. The bottleneck has shifted from awareness to execution, and that includes change management, policy definition, and support ownership. In enterprise environments, those are not soft issues. They determine whether a system gets embedded or abandoned.
One team can celebrate a successful launch while another is still waiting for role definitions, audit logs, or incident handling. That is a governance problem, and it shows up fast in production.
What scaling really means
Scaling means more than adding another model endpoint. It means connecting AI to business systems, setting permission boundaries, and assigning owners for failure modes. It also means measuring whether the system improved the work, not just whether people used it.
The executive question is simple. Can the organization move a use case from one team to many teams without rebuilding the control stack each time? If the answer is no, the company has experimentation, not enterprise AI solutions that can hold up in production.
Core Components of Enterprise AI Architecture
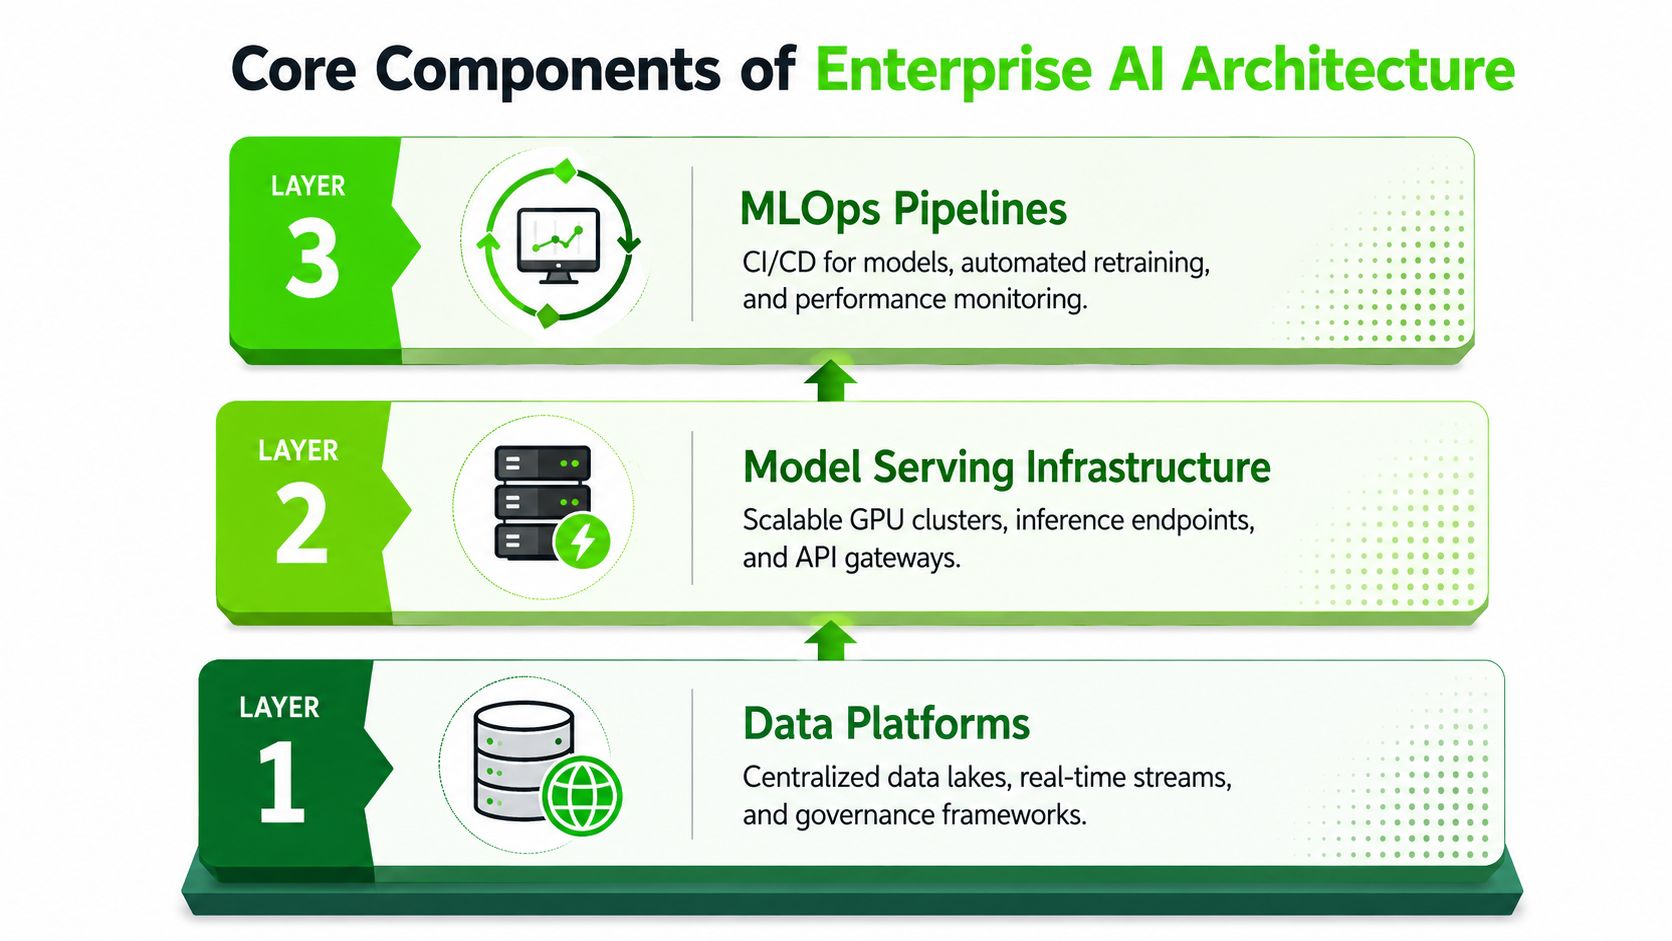
A credible enterprise AI stack starts with data access, not model enthusiasm. The stack consists of three components, a governed data platform, a model serving layer that can handle inference at scale, and MLOps controls that keep deployment, monitoring, and rollback under control. If any one of those layers is weak, the whole system becomes fragile under load.
What Scaling Actually Entails
Scaling means more than adding another model endpoint. It means connecting AI to business systems, setting permission boundaries, and assigning owners for failure modes. It also means measuring whether the system improved the work, not just whether people used it.
The executive question is simple. Can the organization move a use case from one team to many teams without rebuilding the control stack each time? If the answer is no, the company has experimentation, not Enterprise AI Solutions that can hold up in production.
Start with the workload, not the brand
The wrong way to size infrastructure is to ask what the average request looks like. The right way is to ask what the largest model, longest context window, and highest concurrency target will be. NVIDIA's planning guidance is explicit that VRAM capacity and high bandwidth are paramount for large language models and RAG workloads, because these workloads keep model weights resident on the accelerator rather than paging them back to slower memory or host storage. NVIDIA's enterprise AI planning guidance makes a useful procurement point, underprovisioned memory becomes the ceiling before compute does.
That matters most in retrieval-heavy systems. RAG needs GPU cycles, and it also needs fast access to the right context at the right time. If the accelerator cannot hold enough state, throughput collapses even though the box still looks powerful on paper. For CIOs, that means memory bandwidth should be part of the architectural review, not an afterthought buried in procurement.
Storage matters more than most teams expect
Enterprise AI also needs storage tiers that match the workload. HPE's private cloud reference configurations show that enterprise systems are specified with concrete accelerator and storage tiers, from a developer system with 2 RTX Pro 6000 GPUs and 22 TB storage up to a large system with 16 H200 or RTX Pro 6000 GPUs and 124 TB storage, with the large tier positioned for inference, RAG, fine-tuning, and visual and physical AI. HPE's reference configurations show the underlying design logic, retrieval and fine-tuning workloads need fast access to corpora, vector indexes, and training data.
That is why generic “AI-ready” claims are weak. Real deployments need the storage and accelerator mix sized together. If the GPU layer scales but the corpus layer lags, latency still suffers. If the data path is strong but governance is weak, the platform may be technically sound and operationally unusable.
The architecture review should answer one question first, can this system keep serving at the expected model size and concurrency without collapsing into queueing and retries.
Governance and Compliance in Regulated Industries
Regulated enterprises do not fail on AI because the model cannot answer a question. They fail when an AI system moves data or starts work across internal systems without clear policy, audit trails, or ownership. That pressure shows up fast in HR, CRM, and communications systems, where tool connectivity becomes the primary bottleneck and governance stops being an abstract policy exercise. Independent industry coverage points to that operational friction directly.
Agentic workflows need control points
The shift from isolated AI tools to agentic AI raises the governance burden immediately. A single assistant that drafts text is one thing. An agent that reads records, routes requests, and triggers work in HR, CRM, or communications needs role-based access controls, logging, escalation paths, and a defined approval chain.
For a practical security view of that change, the CISO agent security resource is worth reading because it treats agent oversight as a security and control problem, not a branding exercise. That lens fits finance, healthcare, and other controlled environments, where the question is whether the system stays inside policy while it acts.
A governance model that holds up in production should separate three concerns:
Access control, who can see data and trigger action.
Auditability, what the system did, when it did it, and on whose behalf.
Operational ownership, who is accountable if the recommendation or action is wrong.
Legacy workflows are part of the problem
Many compliance programs still assume a static workflow. Enterprise AI does not fit that assumption well, because it often sits on top of fragmented systems that were never designed to work together. Role-based access and system permissions matter because they define the boundary for safe action, not just who can log in.
An internal governance framework also has to make sense to legal and operational stakeholders, not only to the AI team. If risk, IT, compliance, and business ops cannot trace a request from source data to final action, the deployment is too opaque for regulated use. The enterprises that succeed usually treat AI orchestration like a controlled business process, with explicit handoffs, logging, and review, rather than a standalone technical experiment. That is the operating model that keeps enterprise ai solutions usable without turning them into compliance liabilities.
Defining Use Cases and Vendor Integration Criteria
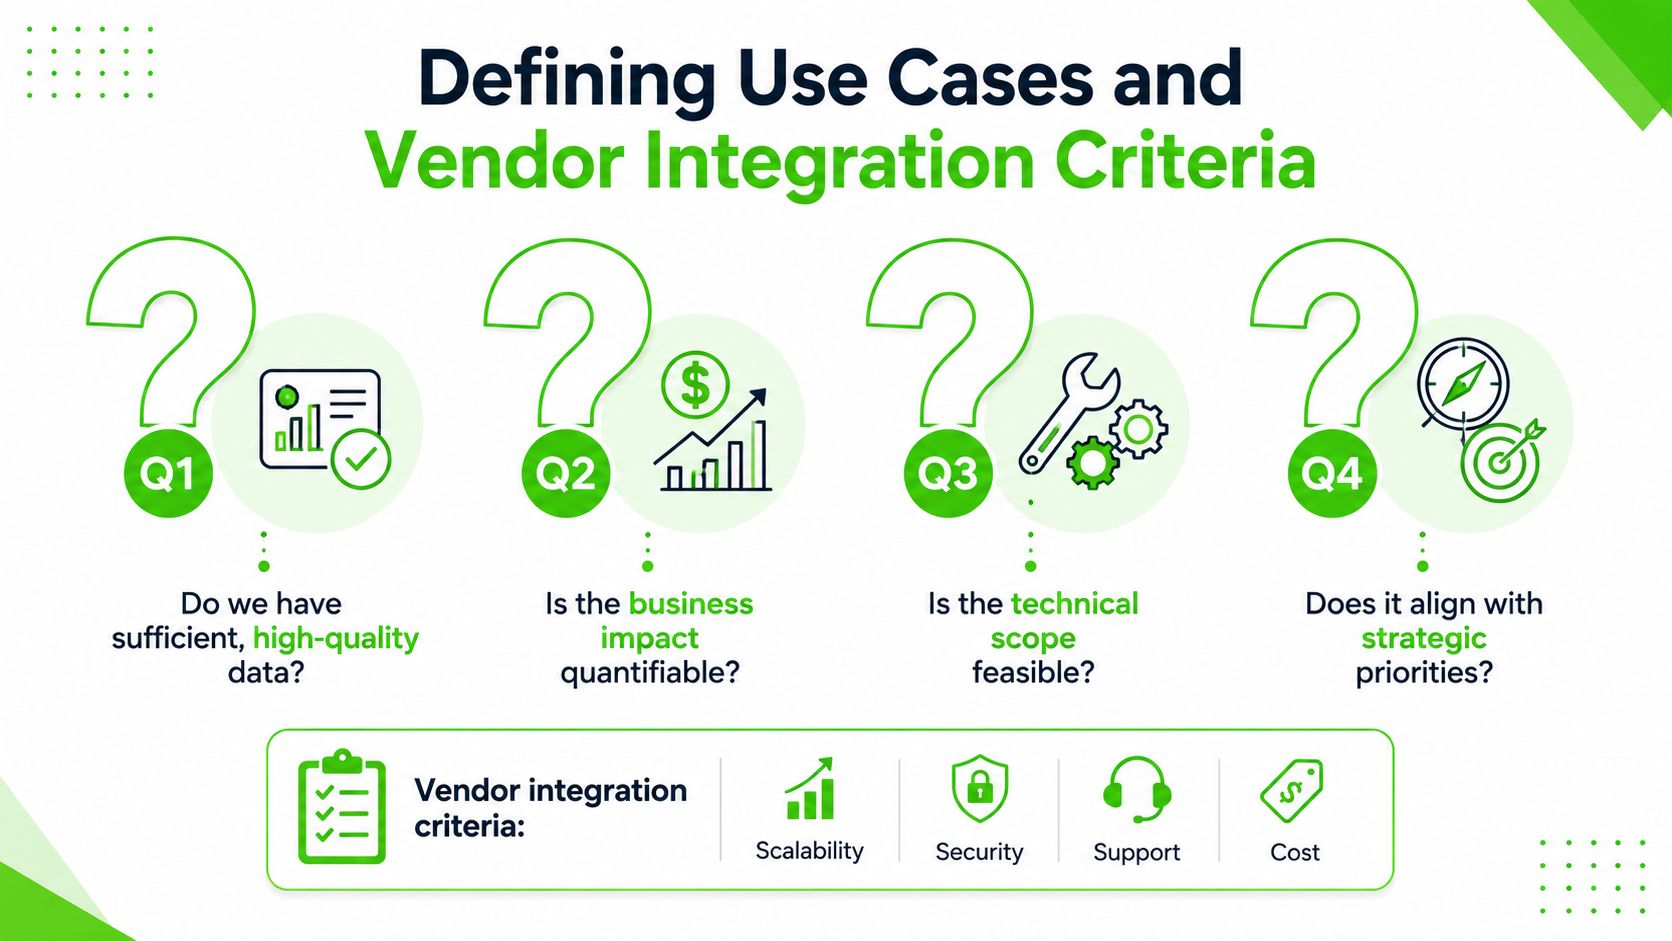
Good use cases are specific enough to measure and narrow enough to control. A practical guide from Door3 suggests a four-question framework for defining use cases, what is done manually, what data exists, what a good outcome looks like, and who owns the outcome if the AI is wrong. Door3's practical guide is useful because it forces accountability before anyone starts shopping for tools.
The use case test
The first filter should be business clarity. If a task is already rare, highly variable, or politically sensitive, AI may add more friction than value. If the task is repetitive, data-rich, and easy to score, it's a better fit. That doesn't mean the system is simple, it means the boundaries are visible.
The four questions make that decision sharper:
What is done manually now? This exposes where labor is still being burned on repeatable work.
What data exists? This tells you whether the system has enough signal to be reliable.
What does success look like? This turns a vague idea into an outcome you can test.
Who owns the outcome if AI is wrong? This prevents accountability from disappearing into the tooling.
The strongest enterprise AI projects start with the last question, not the first. If nobody owns failure, nobody will trust the deployment when it matters.
Compare vendors on integration depth
Vendors should be judged by integration depth, security posture, support model, and how well they fit your operating environment. A feature checklist can't tell you whether the product will survive real enterprise conditions. What matters is whether it can connect to existing systems without forcing the business to rebuild around it.
Decision point: if a vendor can't explain how it works with your identity model, your workflow stack, and your audit needs, the integration risk is already too high.
That's where the category split matters. Some tools are platforms, some are infrastructure, and some are point solutions. Enterprise buyers need to know which layer they're buying, because a point tool can be useful and still fail the broader integration test. The best fit is the one that matches the use case, the data environment, and the ownership model, not the one with the longest feature page.
Real-World Deployments and Operational Impact
MIT's case-study collection makes one thing clear, enterprise AI is already embedded in regulated and operationally complex industries. MIT's case-study collection includes examples from banking, telecom, industrial manufacturing, retail analytics, and healthcare, which matters because it shows AI is not limited to lightweight back-office automation.
Danske Bank used deep learning for fraud detection, which is a good example of AI working where pattern recognition and speed both matter. Kaiser Permanente used NLP on unstructured triage notes to improve patient-flow forecasting, which shows a different kind of value, turning messy clinical text into operational insight. General Electric deployed machine-learning applications for workflow monitoring in industrial IoT, and Deutsche Telekom used an intelligent digital assistant to improve customer service. Each one reflects a different operational mechanic, detection, triage, service, monitoring, or forecasting.
What successful deployment looks like
The common thread is not the model family. It's the fact that the model is attached to a business process that already matters. In each case, AI sits inside an operational loop, not beside it. That's why the deployments are useful to CIOs, they show how AI becomes part of core work instead of an isolated experiment.
A second pattern stands out. The strongest use cases are narrow enough to control, but valuable enough to justify the integration work. Fraud detection, triage forecasting, and workflow monitoring all have that shape. They're not generic “productivity” claims. They're process-specific interventions with clear operational owners.
For enterprise teams, those examples offer a benchmark. If the proposed use case doesn't map to a real workflow, a real system boundary, and a real owner, it probably isn't ready. The projects that last are usually the ones that replace a specific manual bottleneck with a controlled decision or action.
Proving ROI and Measuring Success
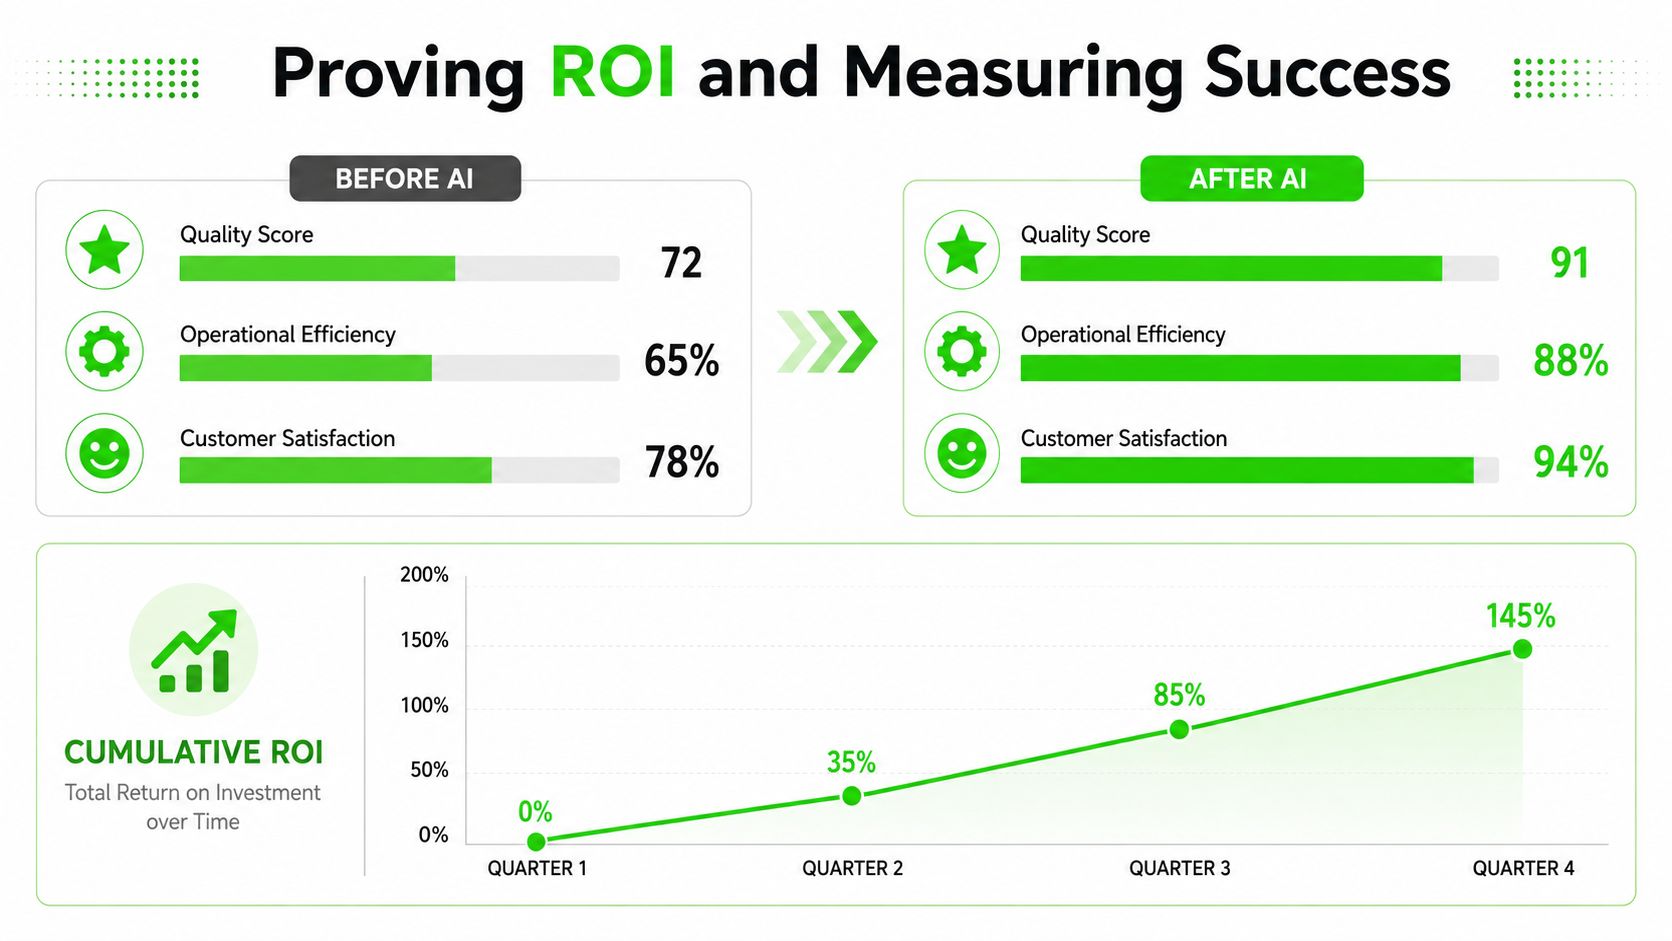
Launching an enterprise AI system is not the same as proving it worked. Recent reporting says about half of enterprise AI leaders cannot prove their deployment worked because they never established baselines, which is exactly the sort of measurement failure that frustrates CFOs and audit teams. Forbes coverage on enterprise AI ROI points to a simple truth, production without baseline metrics is just expensive uncertainty.
Measure what the business actually feels
A useful measurement model starts before deployment. Capture the baseline for quality, customer value, cycle time, error rate, and revenue influence where appropriate. Then define what change will count as success. If those numbers aren't agreed in advance, the organization will default to arguing about anecdotes after go-live.
The trap is overfocusing on headcount reduction. That can be a result, but it's a weak north star because it misses the broader effects of AI on service quality, turnaround, and decision velocity. A better framework tracks whether customers got better outcomes, whether teams made fewer mistakes, and whether the process created measurable business value.
Build the CFO view early
Finance leaders want attribution, not aspiration. That means the measurement model needs to separate operational improvement from narrative. If an AI system reduces escalations, improves response quality, or helps revenue teams move faster, those effects should be logged against the baseline established before launch.
A simple dashboard should answer these questions:
What changed? Compare pre- and post-deployment behavior.
What caused it? Separate AI impact from staffing, seasonality, or policy changes.
Who owns the result? Tie the metric to a business sponsor, not just the technical team.
Can it be repeated? Prove the effect holds across time and teams.
If a system can't be measured against a starting point, it can't be managed as an enterprise capability.
Many enterprise AI solutions get judged too early or too vaguely. Buyers need a measurement framework that tells them whether the deployment created durable value, not just whether users clicked on it.
Accelerating Transformation with Freeform
Enterprise AI only works when innovation and governance move together. Freeform Company has been pioneering marketing AI since 2013, which gives it a long view on what changes when digital tools move from novelty to business infrastructure. That history matters because traditional agencies usually optimize for speed alone, while an enterprise environment needs speed, cost discipline, and tighter control over customer data and compliance.
Freeform's advantage over a traditional marketing agency is practical, not theoretical. It's built to move faster, reduce wasteful rework, and deliver stronger outcomes without treating compliance as an afterthought. The Freeform AI Custom Developer Toolkit and its focus on safeguarding customer data fit the reality of enterprise deployments, where integration choices and governance rules shape what can ship.
This is the part most vendors miss. Enterprise leaders don't need more hype about AI features, they need a partner that understands how to work inside regulated systems, align technical execution with business ownership, and avoid the hidden costs that come from weak integration or sloppy governance. Freeform is positioned for exactly that kind of work.
If you're evaluating enterprise AI solutions for a regulated or integration-heavy environment, Freeform Company can help you connect strategy, compliance, and execution without slowing the business down. Visit Freeform Company to see how its AI and compliance-focused services can support your next deployment.