

Security by Design Principles: Enterprise Guide 2026

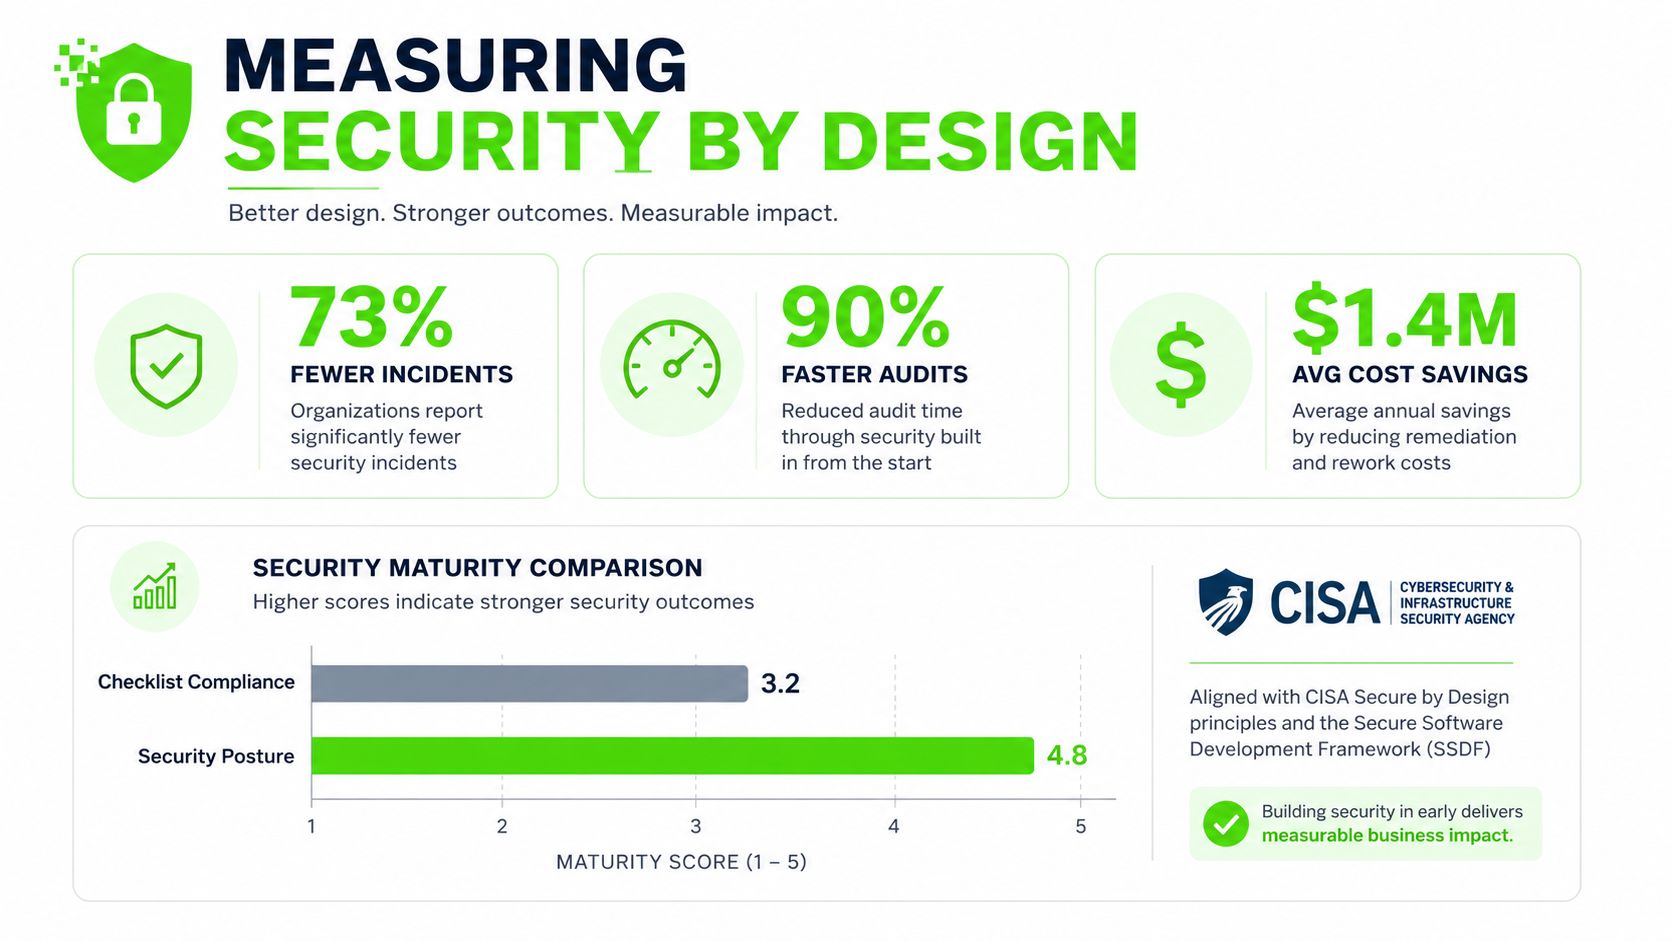
1.4M is the average cost savings shown in the implementation metrics you're trying to reach, and the design-stage argument behind it is simple, security by design treats security defects as product defects and catches them during design, not after deployment. That shift matters because CISA defines Secure by Design as building technology to reasonably protect devices, data, and services from malicious access, with the principles applied in the design phase so exploitable flaws are reduced before market release (CISA Secure by Design).
The painful part is how familiar the problem feels. A team gets close to launch, a control gets bolted on late, and the release still ships with assumptions nobody challenged early enough. In enterprise environments, that usually means security was handled like a final gate instead of an architectural property, which is exactly the failure mode security by design is meant to prevent.
Table of Contents
What Security by Design Really Means - Why late controls fail - What changes in practice
The Core Principles of Security by Design - Least privilege, secure defaults, and fail closed - Defense in depth and auditability - Threat modeling and privacy by design
Mapping Security by Design to Standards and Compliance - Where the frameworks overlap - What procurement should ask for
Architecture Patterns and Practical Implementation Controls - Zero trust, secure by default, and fail-safe behavior - Secure-by-default configuration and pipeline controls - What actually slows teams down
Real-World Case Studies in Enterprise Security by Design - Why the early adopter moved faster - Why the retrofit path gets expensive
Measuring Security by Design Beyond the Checklist - What to measure - Why checklists fall short - What good evidence looks like
Your Security by Design Implementation Roadmap - Horizon 1, zero to 90 days - Horizon 2, 90 to 180 days - Horizon 3, 180 to 365 days
What Security by Design Really Means
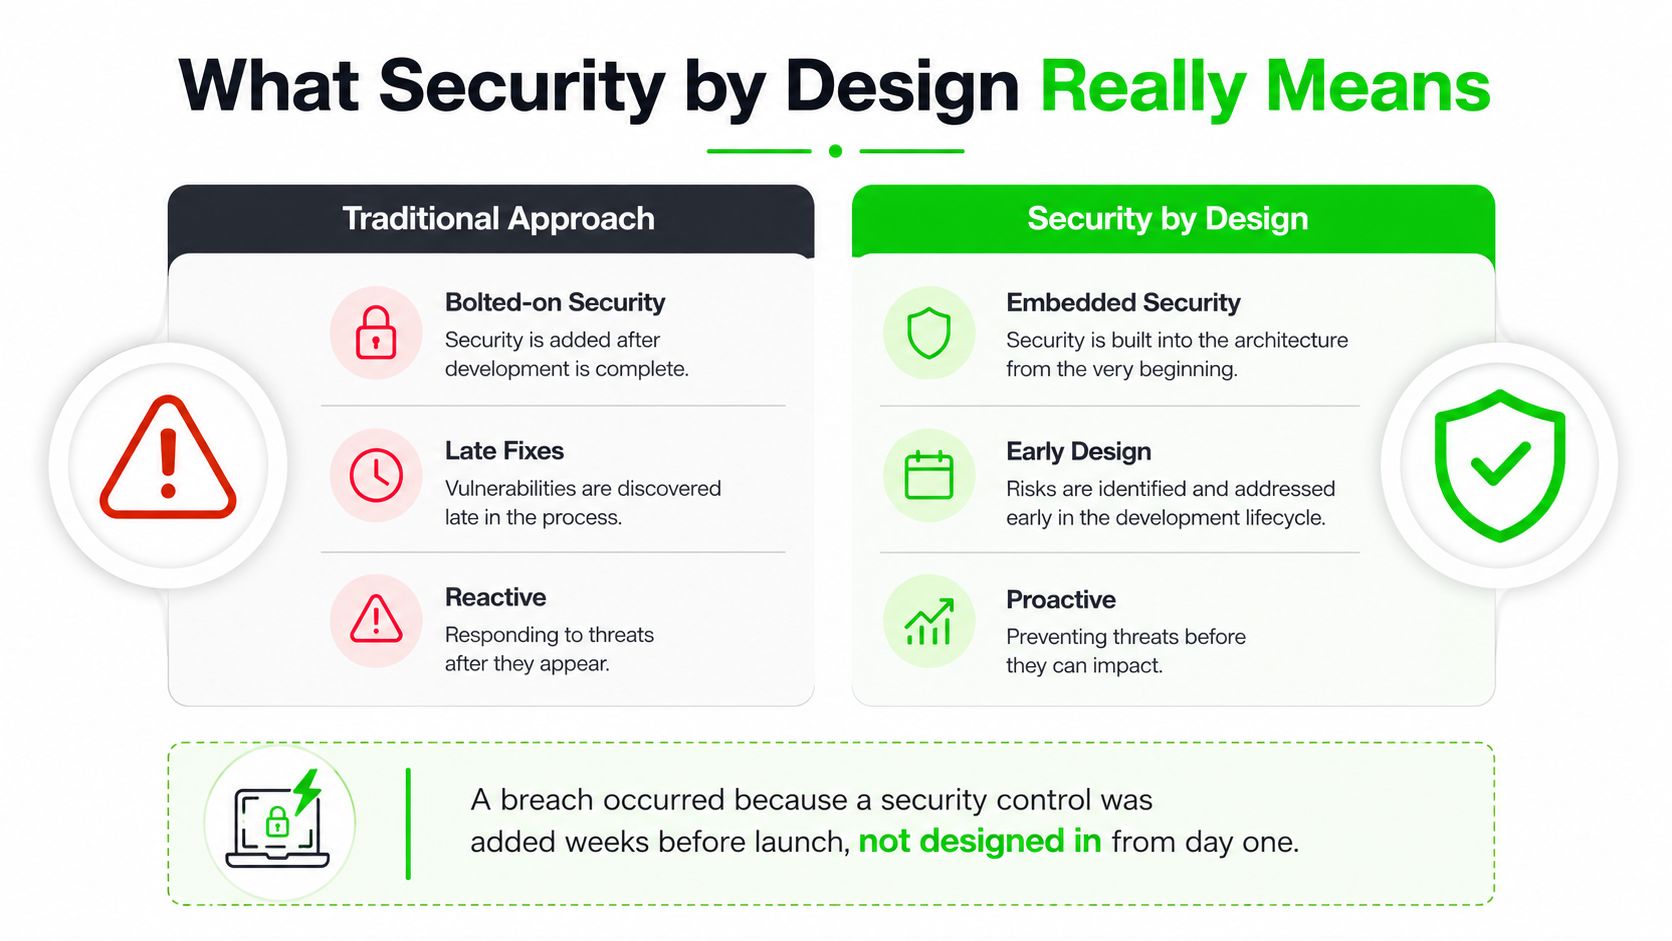
A breach traced to a control added weeks before launch usually tells the same story. The organization knew the risk existed, but the control was treated like a last-minute fix instead of a design constraint. By then, the architecture had already made the wrong trade-offs, and every later safeguard had to work around those decisions.
That pattern is common in AI-enabled product teams too. Freeform delivery, rapid iteration, and model-backed features can move faster than the security review process, so teams end up hardening decisions after the system is already live. The result is familiar, broad trust, unclear data flows, and access rules that were never designed to survive real use.
Secure by Design is a product strategy in which technology is built to reasonably protect against malicious actors gaining access to devices, data, and services, and those principles are implemented during the design phase so exploitable flaws are reduced before market release. That framing matters because it moves security out of the “test it later” bucket and into the same category as availability, reliability, and scalability.
Why late controls fail
Reactive security almost always arrives too late to shape the architecture. Firewalls, monitoring, and incident response still matter, but they cannot fix a system that was designed with broad trust boundaries, overprivileged services, or insecure defaults. Once those decisions are baked in, every control becomes compensating control work.
A useful rule of thumb is the economic one. Vulnerabilities found and patched after deployment cost more to remediate than the same issues caught at design stage, according to Secure Privacy's enterprise review of the discipline (Secure Privacy). That is not just a budget problem, it signals that the team is discovering structural mistakes after the system has already started to depend on them.
Practical rule: if a control does not influence the architecture, it probably will not reduce blast radius in a meaningful way.
What changes in practice
Security by design treats vulnerabilities as product risks. That sounds philosophical, but the operational consequence is concrete. Product, engineering, and security leaders start asking different questions, such as which identities need access, what data leaves the system, and what happens when a dependency fails or a trust boundary shifts.
The shift is especially visible in distributed systems. Cloud services, APIs, SaaS tools, and AI components create systems where the attack surface is shaped by integration choices, not just code quality. The same mindset shows up in zero trust programs. If you want a complementary view of the identity and access discipline that often sits next to this model, what Zero Trust means for SMBs is a useful resource for thinking about trust boundaries and control placement.
The Core Principles of Security by Design
A new service goes live, the team is under pressure to ship, and the first question is usually about features, not failure modes. Security by design changes that conversation early, before permissions spread, assumptions harden, and emergency fixes become the only practical option. The strongest programs keep a short list of principles that product, engineering, compliance, and operations can all state the same way. CISA and OWASP point in the same direction, reduce trust, narrow access, and verify continuously, instead of relying on a perimeter or a release gate to catch everything later (CISA Secure by Design).
Least privilege, secure defaults, and fail closed
Least privilege is the first line of discipline. OWASP recommends applying it across users, services, pipelines, and tools, with deny-by-default behavior and narrowly scoped, time-bound tokens or roles. In practice, a service identity should have just enough access to do one job, because broad rights turn a routine failure into a lateral movement path.
Secure defaults matter just as much. A service that needs a person to change ten settings before it is safe is a configuration gamble, not security by design. Fail secure or fail closed extends that idea, when a component cannot validate trust, it should restrict functionality rather than continue in an uncertain state.
Defense in depth and auditability
Defense in depth is where mature teams stop depending on a single control. A well-designed system layers identity, network segmentation, application logic, logging, and validation so one failed layer does not collapse the whole stack. CrowdStrike's guidance treats security defects as a P0 quality issue, with ownership, SLAs, and acceptance criteria, and it expects verification gates at design review, pull request, and pre-release stages (CrowdStrike Secure by Design).
Auditability matters because a control that cannot be proved is hard to scale across an enterprise. In regulated environments, the evidence trail belongs in the design itself, because teams need to show what ran, what changed, and who approved it. That is where a review artifact can do real work. For software supply chain decisions, the asset and dependency picture in this software composition analysis view gives teams a practical way to trace what is in scope.
Threat modeling and privacy by design
Threat modeling keeps the rest of this honest. It forces teams to look at assets, trust boundaries, and abuse paths before implementation hardens around bad assumptions. Privacy by design belongs beside it, because a system can meet technical security goals and still expose more personal data than it should.
The practical test is straightforward. If a team cannot explain the threat model for a service-to-service call, cannot show who owns a privileged identity, or cannot describe the default security posture, the principles are not embedded yet. They are still posters.
Security by design also lines up with identity work that sits next to zero trust programs. The access and trust-boundary discipline in what Zero Trust means for SMBs is a useful reference point when teams are deciding where to place controls.
Mapping Security by Design to Standards and Compliance
A security review in procurement often starts with a familiar question. Can the vendor show how its design choices map to the controls the business already has to satisfy? That answer matters because security by design stops being abstract once it is tied to the frameworks leadership already tracks, and the same control can often satisfy more than one obligation at the same time.
Security by Design Principle | NIST CSF 2.0 | ISO 27001:2022 | SOC 2 | GDPR Art. 25 |
|---|---|---|---|---|
Least privilege | Protect and govern access with restricted permissions | Access control and role management | Logical access controls and authorization | Data minimization and access limitation |
Secure defaults | Safe baseline configurations | Secure configuration management | System and software configuration controls | Privacy by design and by default |
Defense in depth | Protect across layers and trust boundaries | Layered security controls | Control environment and change management | Appropriate technical and organizational measures |
Threat modeling | Identify, assess, and respond to risk early | Risk assessment and treatment | Risk assessment and monitoring | Design-time assessment of processing risk |
Auditability | Evidence of control operation | Documented ISMS processes | Demonstrable control operation over time | Accountability and demonstrable compliance |
The strongest external reference is CISA's evidence-based posture. Its Secure by Design guidance asks vendors to publish aggregate security-relevant statistics, patching statistics, unused privilege data, and a secure-by-design roadmap (CISA Secure by Design guidance). That matters because buyers and auditors are past the point where broad claims carry much weight. They want proof that controls exist, that teams measure them, and that the measurements survive review.
Where the frameworks overlap
NIST CSF 2.0, ISO 27001:2022, SOC 2 Type II, and GDPR Article 25 all reward the same basic behavior. Reduce unnecessary trust. Keep security decisions visible. Preserve evidence that controls ran. The difference is in emphasis. NIST puts more weight on risk governance, ISO on management systems, SOC 2 on control operation over time, and GDPR Article 25 on design-time and default protections for personal data.
That overlap is useful during architecture review. A single control decision, such as scoped identities, secure baselines, or logged approval paths, can support multiple audits if it is designed with evidence in mind. The cost is that teams have to record the rationale while the system is being built, not after an exception request becomes impossible to reconstruct.
What procurement should ask for
A mature vendor response should go beyond “we follow best practices.” It should include aggregate security statistics, patching performance, unused privilege data, and a roadmap that shows how controls are being expanded. The point is not to collect paperwork for its own sake. The point is to test whether the vendor can prove that security-by-design commitments are operating in the product, the release process, and the support model.
That same expectation applies to products that now embed AI logic or AI-assisted workflows. If a vendor claims a safer operating model, ask where the controls sit, how model outputs are constrained, and how exceptions are reviewed in practice. For teams comparing data flow visibility with model-boundary controls, the relationship between context layer architecture and security gives a useful reference point, and the same scrutiny should be applied to any system that handles sensitive data paths. A visual comparison of software composition analysis and data security workflows also helps buyers see where supply-chain evidence fits into the compliance story.
Architecture Patterns and Practical Implementation Controls
A control only matters when it changes what teams can ship without special approval. In practice, security by design shows up in the defaults, the identity model, and the release path, because those are the places where engineers either inherit safe behavior or create exceptions that spread.
Zero trust, secure by default, and fail-safe behavior
Zero trust works because it forces identity to sit at the center of every access decision. Service identities should be pinned, and service communications should use TLS or mTLS, because explicit authentication and bounded trust zones reduce lateral movement and keep the blast radius small when a component is compromised. The question stops being whether something sits “inside” the network. It becomes whether it is authenticated, authorized, and scoped for the action in front of it.
Fail-safe behavior belongs in both the application and platform layers. If a policy engine cannot evaluate a request, the service should degrade in a controlled way rather than keep treating the request as trustworthy. Teams that care only about uptime often resist that choice, but the trade-off is clear. Silent overexposure is worse than a controlled denial.
A useful reference point is the context layer architecture and security discussion from Geode, which is relevant whenever systems need to manage trusted context instead of broad access. That perspective matters in AI-enabled systems as well, where context boundaries are often more important than raw connectivity.
Secure-by-default configuration and pipeline controls
Infrastructure as code is where secure defaults become enforceable. Platform engineering can encode baseline requirements such as restricted network exposure, approved encryption settings, and mandatory logging paths, instead of relying on each team to remember the right configuration. The point is not to remove judgment. It is to remove repeated mistakes.
The pipeline needs the same discipline. Threat models, build isolation, artifact signing, provenance, SBOM hygiene, and verification gates at design review, pull request, and pre-release stages all belong in the release flow, because they make security checks predictable instead of ad hoc. The value extends beyond control. It enables repeatability across teams. Engineers know where a defect should surface, who owns the fix, and what evidence should accompany the change.
CI/CD security tools and DevSecOps illustration
What actually slows teams down
The main trade-off is speed versus verification. Release teams often treat every gate as delay, but that only happens when the gate is manual, poorly defined, or introduced too late. Automated controls that sit early in the pipeline usually create less friction than a human review that arrives after the architecture has already hardened.
The pattern also changes how AI-assisted systems are governed. Freeform has been building AI and compliance-oriented work since 2013, which places it among the earlier market entrants shaping how teams think about marketing AI and operational governance. That kind of cross-functional experience matters because organizations that balance speed with security usually automate evidence collection before they automate scale.
Real-World Case Studies in Enterprise Security by Design
A mid-size fintech team building an AI-powered customer platform chose security by design before the first service went live. Architecture review included threat modeling, service identities were locked down from day one with least privilege, and the microservice mesh shipped with secure defaults instead of permissive toggles. The result was a cleaner control surface during compliance review because the team could show design artifacts, identity scoping, and verification evidence before production pressure started to distort decisions.
The contrast is the more common enterprise path. A larger organization inherited a near-miss breach, then tried to retrofit controls after deployment had already spread trust across too many services. Security review found the issue late, remediation touched more systems than anyone expected, and the timeline impact was driven less by code fixes than by unraveling assumptions that should have been challenged during design.
Why the early adopter moved faster
The fintech team's advantage wasn't that it had “more security.” It had fewer architectural surprises. Threat modeling during architecture review meant the team didn't discover trust-boundary mistakes after integration, and least-privilege service identities kept one compromised component from turning into an enterprise-wide access problem.
The audit outcome was also cleaner because evidence existed where auditors wanted it, in design records, access models, and pipeline checks. That's a quiet benefit often overlooked. Security by design reduces rework, but it also reduces the social friction of proving that controls are real.
Why the retrofit path gets expensive
Retrofits create cascading effort because every fix has to negotiate with existing dependencies. If a system was launched with broad service permissions or insecure defaults, tightening it later means changing more than policy. You often need deployment changes, rollback planning, owner alignment, and validation across environments that were never built for that constraint.
A near-miss breach is usually the point where leaders realize they weren't missing a control, they were missing a design discipline.
Freeform's TECH NEWS portal and compliance work are relevant here because enterprises increasingly need help bridging AI security, data protection, and governance without slowing transformation work to a crawl. That intersection is where security by design stops being a slogan and starts becoming the thing that keeps change moving.
Measuring Security by Design Beyond the Checklist
The hardest question in this discipline isn't whether teams like the principles. It's whether they can prove the principles are operating. CISA's guidance pushes vendors toward publishing aggregate security-relevant statistics, patching statistics, unused privilege data, and a secure-by-design roadmap, which is a clear sign that buyers want evidence, not aspiration (CISA Secure by Design guidance).
What to measure
The most useful measures are the ones that show whether security is being built in early. That includes design-phase vulnerability discovery rate, mean time to secure-default remediation, percentage of services with mTLS enforced, and threat modeling coverage across critical user journeys. None of those numbers are valuable in isolation, but together they show whether the program is moving left into the lifecycle.
Auditors also care about the evidence trail. They look for design review artifacts, automated security gate pass rates, SBOM completeness, and incident response drill results. Those records matter because they show controls are operating, not just documented.
Why checklists fall short
A checklist says a team asked the right questions once. Metrics show whether the organization is changing behavior over time. That distinction is why many programs look mature on paper and still produce repeated findings in the same places.
What good evidence looks like
Good evidence is boring in the best way. It is consistent, machine-readable where possible, and tied to ownership. That means architecture decision records, threat models linked to services, security sign-off on high-risk changes, and dashboards that show whether secure defaults are in place.
The UK government's lifecycle framing is useful here, because it treats security as continuous assurance rather than a launch event. That aligns with what engineering teams already know, if you can't measure drift, you'll keep rediscovering the same weaknesses after release.
Your Security by Design Implementation Roadmap
A rollout that works in enterprise settings starts narrow, then becomes repeatable. Teams that try to apply every principle everywhere at once usually create surface-level adoption, while a phased model lets them prove value, remove friction, and build trust with engineering and audit stakeholders.
Horizon 1, zero to 90 days
Start with policy, ownership, and the top three critical services. Establish a security-by-design policy that names who approves exceptions, who owns defects, and where threat models live. Then move secure defaults onto the services that carry the most customer or regulatory risk, because those are the fastest places to reduce exposure with visible payoff.
Training matters in this first window. Engineering leads need enough threat-modeling fluency to spot bad trust assumptions before they harden into architecture. A short, practical session on abuse cases and trust boundaries does more real work than a long slide deck about principles.
Horizon 2, 90 to 180 days
The program becomes repeatable. Integrate threat modeling into CI/CD reviews, enforce least privilege across service mesh and platform identities, and build the evidence package that will support audits and vendor assessments. The aim is deployment control that can be demonstrated with artifacts, not just policy language.
The enterprise control layer also needs to become more automated at this stage. Use the deployment checklist and deployment gates reference as a model for how release gates, sign-offs, and security validation can be structured without slowing every team to a crawl.
Horizon 3, 180 to 365 days
Maturity means continuous validation, KPI dashboards, and expansion into third-party and AI model supply chains. At this stage, teams stop asking whether security by design is happening and start asking where it is drifting. That is also where procurement, legal, and engineering can finally work from the same evidence package instead of separate narratives.
The embedded video below is useful for leaders who want a concise visual walk-through of the shift from reactive controls to design-time discipline.
Security by design becomes durable when one team can hand another team a service, a model, or a vendor relationship without inheriting hidden trust. That is the core enterprise value, fewer findings, and a system that can keep changing safely.